
Risk Management in QMS: Identifying and Controlling Process Risks
Your QMS has procedures for everything, but does it have a plan for when those procedures fail?
That's where Risk Management Processes come in.
Risk Management is not just about identifying risks associated with medical devices. It is also about identifying what could go wrong within processes that keep your QMS working.
Some questions regarding this might arises:
- What if an employee is not trained to perform an assigned task?
- What if an outdated procedure is used because document revision is not controlled?
- What if a supplier fails to meet agreed quality requirements?
These are not just operational problems; they can affect QMS effectiveness, regulatory compliance and product quality.
How to Identify and Manage Risks in QMS Processes
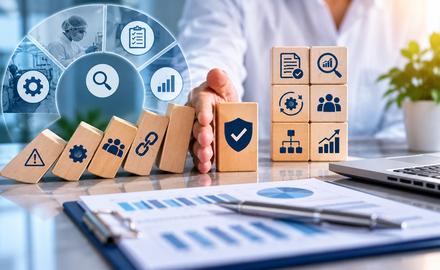
Identify risk in each QMS process. Evaluate what impact that risk could have. Put in place controls that fit the risk. Check whether those controls are working.
A practical approach includes:
-
Identify potential risks: Determine what could go wrong in each process.
-
Evaluate the impact: Assess how each risk could affect product quality, compliance, or QMS effectiveness.
-
Implement controls: Establish measures that are proportionate to the identified risks.
-
Monitor effectiveness: Review whether the controls are working as intended and take further action when necessary.
For example:
Risk from using a document can be lowered by keeping a revision history, limiting who can access the document and removing obsolete versions from use.
Remember, risk management is not something you do once and forget. Audit results, customer feedback, nonconformities and any changes to processes can all bring up risks. These need to be reviewed and reassessed regularly.
Where can QMS risk hide?
Risks can exist in almost every process within a Quality Management System. Identifying these weaknesses early helps organizations prevent recurring problems and maintain compliance.
- Internal Quality Audit (IQA) - the audit planning is not good enough. There are problems that keep happening and are never really fixed.
- Management Review (MRM) - No one is clear about what they need to do when they need to do it or if they need to check back later.
- Training - employees are doing their jobs. They don't have the right skills or knowledge to do them properly.
- Document Control - old procedures are still being used. Important papers are lost and can't be found.
- Supplier Management - suppliers are not meeting the quality standards that were agreed on.
- CAPA - actions are taken to fix the problem. They won't stop it from happening again.
- Change Control - changes are made without checking how they affect the quality management system.
- Data Analysis - the information used is wrong which leads to choices being made.
Example
Your internal audit identifies the same nonconformity for the third time.
Closing the audit finding may seem like enough. But what if the root cause remains? The problem could return in the next audit.
The risk-based approach asks: Why does this keep happening, what could it affect and what action will prevent it from happening. That is the difference between writing down a problem and dealing with the risk that comes with it.
How Does Risk-Based Thinking Help Prevent Recurring Nonconformities?
Consider a situation in which an internal audit identifies the same nonconformity for the third time.
Closing the audit finding may appear sufficient. However, if the root cause remains unresolved, the problem could return during the next audit.
A risk-based approach encourages organizations to ask three important questions:
- Why does this problem keep happening?
- What processes, products, or compliance requirements could it affect?
- What actions are needed to address the underlying cause and prevent recurrence?
For example, if employees repeatedly use outdated procedures, the issue may not simply be employee error. It could indicate weaknesses in document distribution, access permissions, training, or change communication.
Investigating these underlying risks helps organizations develop more effective corrective actions rather than repeatedly treating the same symptoms.
When Should QMS Risks Be Reviewed?
Risk assessments should be reviewed when new information or changes could affect the effectiveness of existing controls.
Common triggers include:
- Recurring audit findings or nonconformities.
- Customer complaints and feedback.
- Supplier performance issues.
- Changes to processes, equipment, software, or procedures.
- New regulatory requirements or changes in applicable standards.
- Evidence that existing risk controls are ineffective.
Regular reviews help organizations keep their risk management activities relevant and ensure that emerging issues are addressed before they develop into larger problems.
Key Takeaway
A strong QMS doesn't wait for problems to turn into issues. It identifies potential weaknesses, evaluates their impact, and takes appropriate action before they grow.
Because quality management isn't just about controlling what went wrong. It's about anticipating what could go wrong.
V Reg Solutions supports organizations in strengthening their Quality Management Systems through quality and regulatory consulting, helping them address process risks, improve compliance practices, and build more effective quality management processes.
By adopting a proactive, risk-based approach, organizations can move beyond simply maintaining documented procedures toward building a QMS that works effectively in practice.
Share this blog
Read More Blogs
SAHPRA Medical Device Registration: Step-by-Step Guide
Quality Policy: More Than Just Words on a Wall